







As AI continuing to develop at a rapid pace and legal frameworks try to keep pace, companies in the EMEA region (Europe, Middle East, and Africa) are squeezed between both a burgeoning array of cybersecurity threats and regulatory demands. These organizations must navigate through a maze of compliance frameworks to protect data, build customer trust, and avoid hefty penalties.
This guide looks into the intricacies of managing compliance across key frameworks—PCI DSS, ISO 27001, HIPAA, HITRUST, GDPR, DORA, NIS 2, and Cyber Essentials—for EMEA companies to effectively manage their compliance efforts.
Decoding the relevant compliance frameworks
Before diving into the nitty-gritty, here’s a reminder of the frameworks that are important:
PCI DSS
The Payment Card Industry Data Security Standard (PCI DSS) is essential for any organization in EMEA that is handling credit card transactions. This framework secures credit and debit card transactions against data theft and fraud. For example, an e-commerce company based in France must implement PCI DSS to safeguard cardholder data, ensuring all transactions are encrypted and securely processed. Compliance prevents costly data breaches and fortifies customer confidence in the company’s payment systems.
ISO 27001
ISO 27001 is recognized globally for setting the benchmark for an information security management system (ISMS). It provides a systematic approach to managing sensitive company information, ensuring it remains secure. Adopting ISO 27001 can help EMEA businesses protect their information assets and manage security in a comprehensive way. For instance, a German manufacturing firm might implement ISO 27001 to secure its intellectual property and customer data, thus enhancing its reputation and compliance stature.
HIPAA
Although The Health Insurance Portability and Accountability Act (HIPAA) is a U.S. regulation, it has implications for EMEA companies that deal with the health data of U.S. citizens. This is particularly relevant for companies like cloud service providers based in the Netherlands that store and process health information from U.S. healthcare entities. Ensuring HIPAA compliance helps these companies avoid legal pitfalls and fosters trust with their international partners.
HITRUST
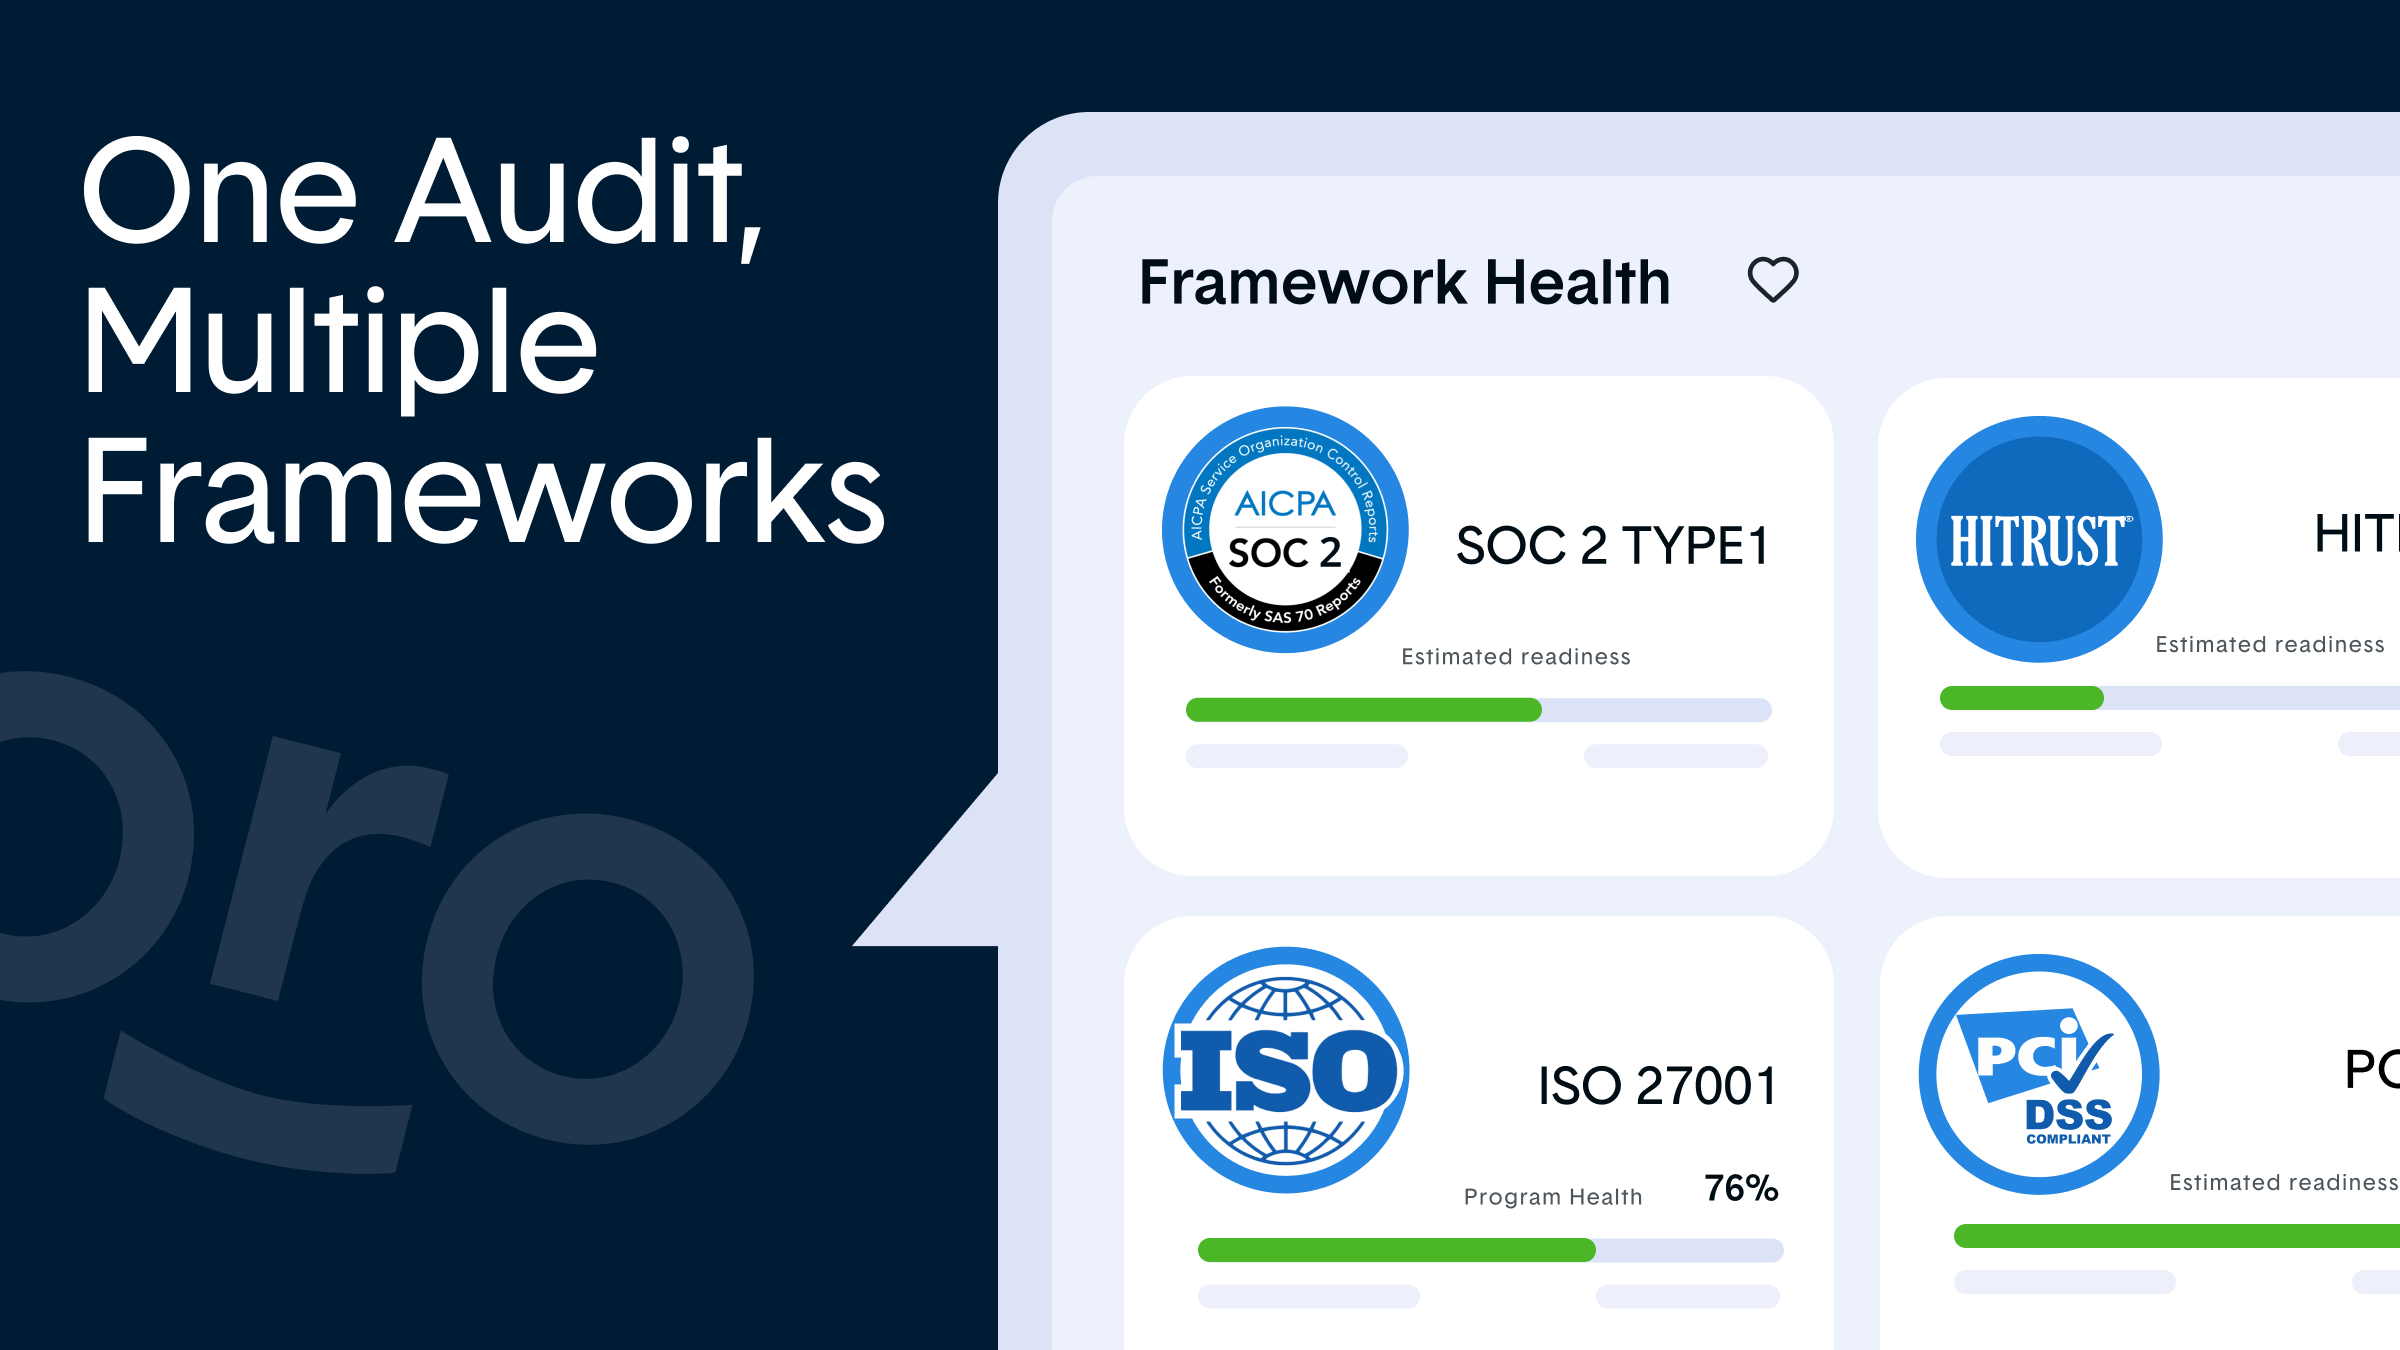
There are many redundancies and overlap of controls across the above frameworks. This is where HITRUST can shine.
HITRUST integrates various cybersecurity frameworks and regulatory requirements, making it a robust framework for companies that need to comply with multiple standards. For an EMEA healthcare software provider, for example, leveraging HITRUST can streamline compliance with both international regulations, like HIPAA, and various standards thereby simplifying the compliance process through a unified approach.
GDPR
Perhaps the most recognisable and widely-discussed framework in EMEA, or within the EU at least, is the General Data Protection Regulation (GDPR). Following these regulations is pivotal for any business operating within the EU or dealing with EU residents’ data.
GDPR emphasizes transparency, security, and accountability by businesses, demanding strict controls over data processing and movement. A South African bank with EU customers, for example, must comply with GDPR to handle personal data lawfully and avoid potential fines of up to 4% of annual global turnover or €20 million, whichever is higher.
And now we have some newer regulatory frameworks such as:
DORA
DORA (Digital Operational Resilience Act) applies to financial institutions across the EU, mandating robust cyber resilience practices to ensure operational stability.
NIS 2
NIS 2 (Network and Information Security Directive) targets essential service providers, like utilities and healthcare, within the EU, enforcing strong cybersecurity and incident response capabilities.
DORA and NIS 2 set concrete requirements for companies in the EU’s financial and essential services sectors, ensuring these sectors maintain high resilience and strict incident response protocols.
Cyber Essentials
Cyber Essentials is a government-backed certification that promotes basic cybersecurity practices, making it a practical tool for companies of any size to defend against common cyber threats.
Cyber Essentials is specifically designed for UK-based companies, while DORA and NIS 2 target organizations within the EU.
Regulatory frameworks like DORA, NIS 2, and Cyber Essentials provide more explicit requirements, simplifying compliance for companies while ensuring standardized protection measures.