






Information security permeates every level of an organization and is a critical step that safeguards its most valuable asset—data. At the forefront of information security management systems (ISMS) stands ISO 27001.
ISO 27001 is a compliance standard, but its benefits go beyond those of security. It can also be key in unlocking new business opportunities and fostering trust with customers and stakeholders. In this blog post, we’ll delve into the full benefits of ISO 27001, unraveling its importance in enhancing your organization’s information security.
Key takeaways
- ISO 27001 certification provides organizations with a standard to evaluate and improve their security processes, build trust with customers, mitigate risks, streamline processes & reduce errors
- It helps organizations attract new business by demonstrating a commitment to information security and compliance with legal/regulatory requirements
- ISO 27001 enables organizations to effectively respond to evolving threats while improving overall security awareness across the organization
First: Understanding ISO 27001 and its importance
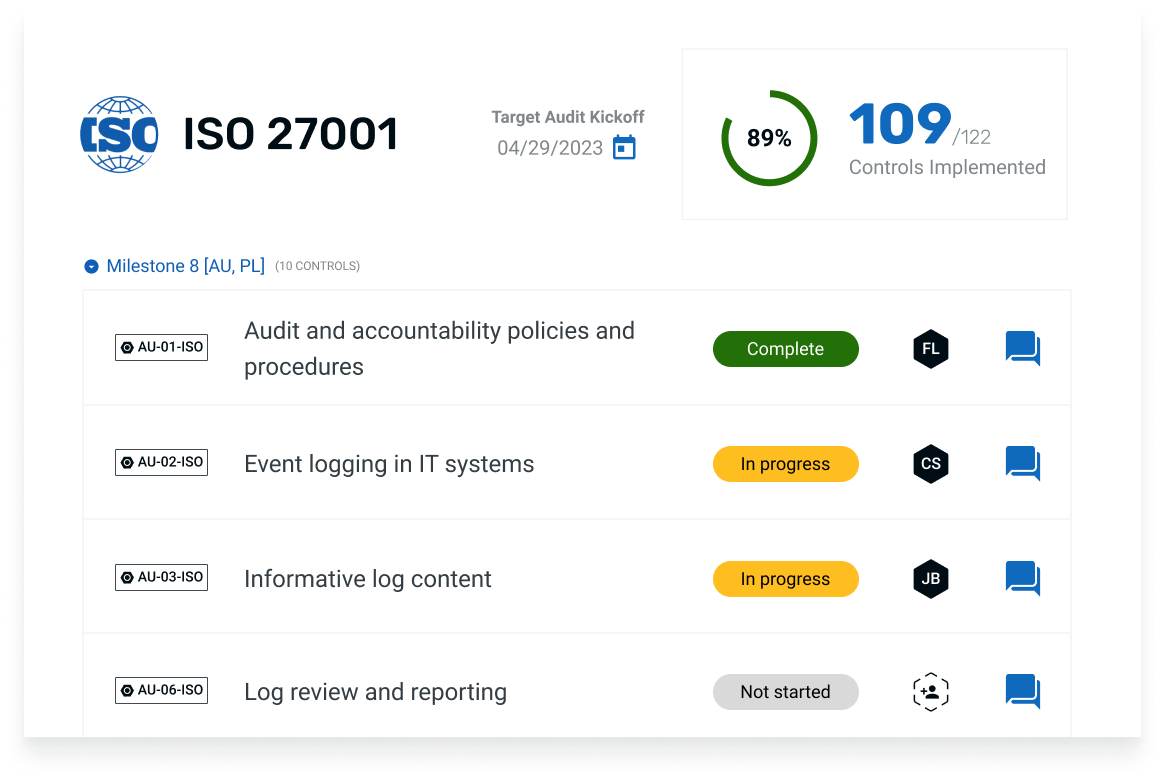
ISO 27001 is the internationally recognized standard for information security management systems (ISMS). It offers a structured framework that assists organizations in safeguarding their assets, demonstrating their dedication to information security, and enhancing security effectiveness.
By utilizing ISO 27001, organizations can effectively manage their information security risks, adhere to legal and regulatory requirements, and optimize their business processes.
Notably, ISO 27001 is the only auditable international standard for ISMS, equipping organizations with the means to evaluate and improve their security processes and strategies. Any organization that handles sensitive data, regardless of its size, may contemplate achieving ISO 27001 certification. It’s a beacon of trust, a testament to an organization’s commitment to protecting sensitive data from cyber-attacks and security breaches.
Let’s look at some of the key benefits of ISO 27001 compliance for any organization.
1. Attract new business and employees
In the fiercely competitive business landscape, ISO 27001 certification can help set you apart from your competition. It substantiates your organization’s claims of rigorous information security practices, offering a competitive edge and opening up new business opportunities. Indeed, ISO 27001 may even be a requirement for some partnerships or B2B relationships.
Not only does ISO 27001 certification demonstrate an organization’s dedication to information security, but it also serves as a proven marketing edge. Similarly, in a competitive talent market, having standards like ISO 27001 and a stellar reputation will set your organization apart for top-notch job candidates.
While, of course, many other factors go into success in closing new business or successful recruitment processes, when all else is equal, ISO 27001 may give you that competitive edge.
2. Build trust with customers and stakeholders
In the business world, trust forms the foundation of enduring relationships. ISO 27001 certification serves as a testament to an organization’s commitment to safeguarding against cyber threats, thereby fostering trust with customers and stakeholders.
Demonstrating good security practices
By adhering to the requirements of ISO 27001, organizations can demonstrate their dedication to data security, recognize potential security deficiencies and susceptibilities, and augment their cyber resilience.
Additionally, ISO 27001 encourages a culture within an organization that is conscious of security. It provides a systematic approach to managing things like information security, enabling the formation of a system that ensures all parties maintain their focus on information security tasks. This results in a more productive and efficient workflow, reducing the likelihood or impact of security breaches or cyber-attacks.
Take Cinchy, for example. Cinchy’s core values of data centricity and autonomous data translate directly into their commitment to keeping their customers’ information safe and secure. That’s why they partnered with Thoropass as a thorough and efficient way to achieve both SOC 2 and ISO 27001 compliance. According to Saskia Bec, Infosec Analyst at Cinchy, “having the reports in our hands alleviates any concern from our customers.”
Certification of ISO 27001 can make a huge difference in minimizing financial and reputational risks: Organizations can reduce the likelihood of data breaches by implementing robust security measures and controls. This, in turn, minimizes the risk of costly litigation and consequential financial penalties.
With the global average cost of a data breach in 2023 standing at a staggering $4.45 million (IBM), the importance of robust information security cannot be overstated.
Avoiding regulatory fines
Failing to comply with various data protection regulations can have severe consequences for organizations, including hefty fines. ISO 27001 certification can assist organizations in avoiding such penalties by ensuring compliance with data protection requirements.
ISO 27001 certification can help organizations avoid such pitfalls by providing a framework for implementing and maintaining an effective ISMS, thereby preventing data breaches and demonstrating compliance with regulatory requirements.
4. Streamline security processes and reduce human errors
Implementing ISO 27001 not only fortifies an organization’s security stance but also makes its security processes more efficient through the application of proportionate security controls. It fosters the creation of documented procedures, which in turn leads to a more effective and efficient workflow.
Moreover, ISO 27001 certification can significantly reduce the potential for human error, a common cause of security incidents and data breaches. By implementing structured and standardized security processes, organizations can minimize the risk of unintentional errors leading to security breaches, thereby enhancing their overall security effectiveness.
5. Achieve compliance with legal and regulatory requirements
Navigating through the maze of legal and regulatory requirements can be challenging for any organization. ISO 27001 certification can prove to be a valuable compass, guiding organizations to enhance their compliance with these requirements.