Scaling your HealthTech compliance program: The ultimate resource
August 29, 2023
For HealthTech leaders with a hundred questions about infosec security, there are probably 101 separate answers. Finding the correct information is hard enough, while knowing how much of it to implement is the next challenge.
We’ve solved both issues for you in one place:
Find your best path to compliance
Scale your HealthTech compliance program with a multi-framework approach
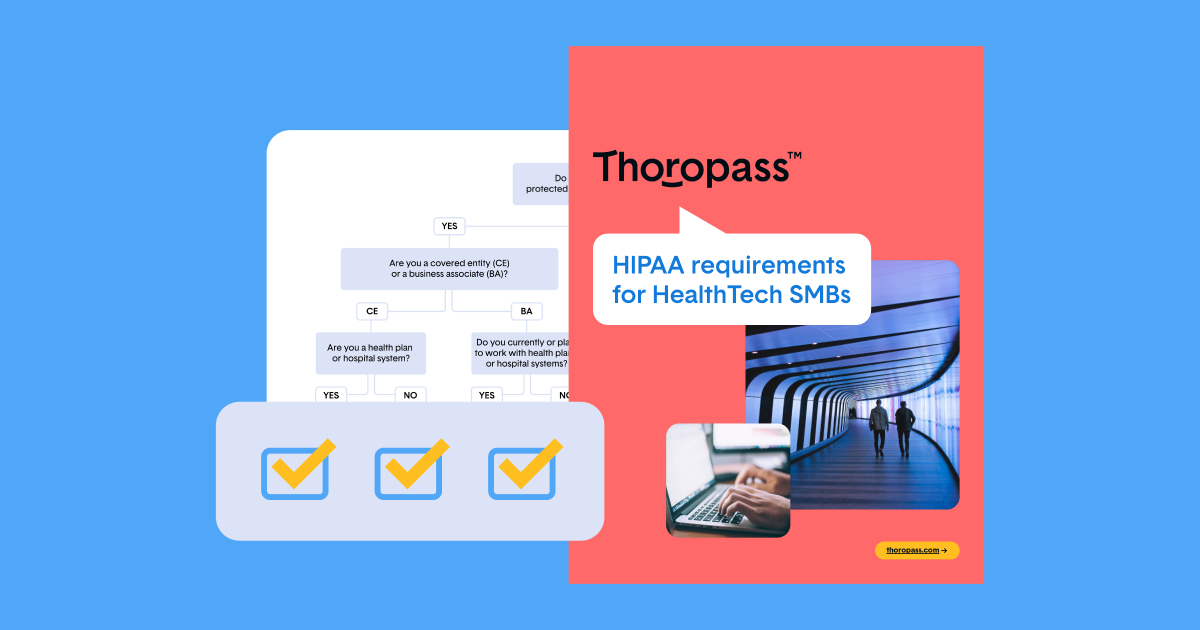
Our latest strategy guide is part roadmap, part collection of relevant sources, and all meant to get you compliant and into new deals and markets as quickly as possible.
SOC 2, HIPAA, and HITRUST compliance software increasingly compete for attention in today’s HealthTech markets. We’ve cut through the noise to help you pick which compliance framework(s) you need, and point you to when you need them.
So why establish and expand your compliance program now with one or more frameworks? As HITRUST expert, Zach Rutz, explains.
Achieving compliance across multiple frameworks enhances your company’s trustworthiness and credibility among customers, partners, and regulatory bodies in the market and sales process.”
Zach Rutz
Manager, HITRUST Assurance
Thoropass
In the HealthTech industry, data breaches cost a hefty sum. IBM recently reported that HealthTech data breaches had an average price tag of $10.1 million dollars in the last year alone. Implementing one or more frameworks is your best bet to protect and secure your organization from a cyber incident or mishandling of data now (and in the future).
For HealthTech companies, many certifications and attestations may benefit your business. With more frameworks come more controls, but also more opportunities. And the good news is there can be overlap from one framework to another. From SOC 2 to HIPAA and HITRUST, you can drive your business to scale, close deals, and secure partners by implementing vital frameworks.
HealthTech companies can benefit from saved time, money, and resources by utilizing an initial audit to start multiple frameworks. Peach, a company in the HealthTech industry, is a great example of a multi-framework approach to compliance. Their story of managing and leveraging their HIPAA, SOC 1, and SOC 2 offers insight into why demonstrating trust with a more robust compliance program is an impactful business advantage.
Developing a compliance roadmap that is just as unique as your company, and that is designed to meet your specific organizational goals is essential. To save you time from seeking out answers from multiple sources, we’ve compiled everything you need to know into this one offer to get you the roadmap you need to get to the success you deserve.
To fully understand the world of infosec compliance for HealthTech, learn which frameworks suit your growing business, and your custom roadmap to achieve your compliance goals, check out this collection of curated content for HealthTech leaders.
In this post:
Stay Connected
Subscribe to receive new blog articles and updates from Thoropass in your inbox.
Find your multi-framework mix
Discover what makes sense for your business to stay compliant.
Build your roadmap to pursue the best frameworks for your HealthTech company and know when to leverage them.
Reducing risk and increasing ROI: why new industries are increasingly turning to HITRUST for certification
For years, HITRUST certification has been closely tied to healthcare. But we recently sat down with Ryan Patrick, VP of Market Research and Strategy for HITRUST, to learn more about the certification and how they’re supporting organizations across a much wider range of industries. From reducing risk to unlocking new business opportunities, HITRUST has become a standard worth considering regardless of your sector. Here are the main takeaways from our conversation.
InfoSec teams have bigger ambitions than simply ticking off checkboxes to stay compliant. They want to drive real business outcomes for their organization—yet too often they’re stuck in a cycle of reactive firefighting, scrambling through audit seasons, and being viewed as a cost center that slows down deals rather than accelerating them.
Laika Compliance, LLC dba Thoropass Assurance is a licensed certified public accounting firm registered with the American Institute of Certified Public Accountants (AICPA). Thoropass, Inc. dba Thoropass is a leading cybersecurity and compliance professional services and technology firm.
Scaling your HealthTech compliance program: The ultimate resource
Thoropass Team
August 29, 2023
•
5 min read
For HealthTech leaders with a hundred questions about infosec security, there are probably 101 separate answers. Finding the correct information is hard enough, while knowing how much of it to implement is the next challenge.