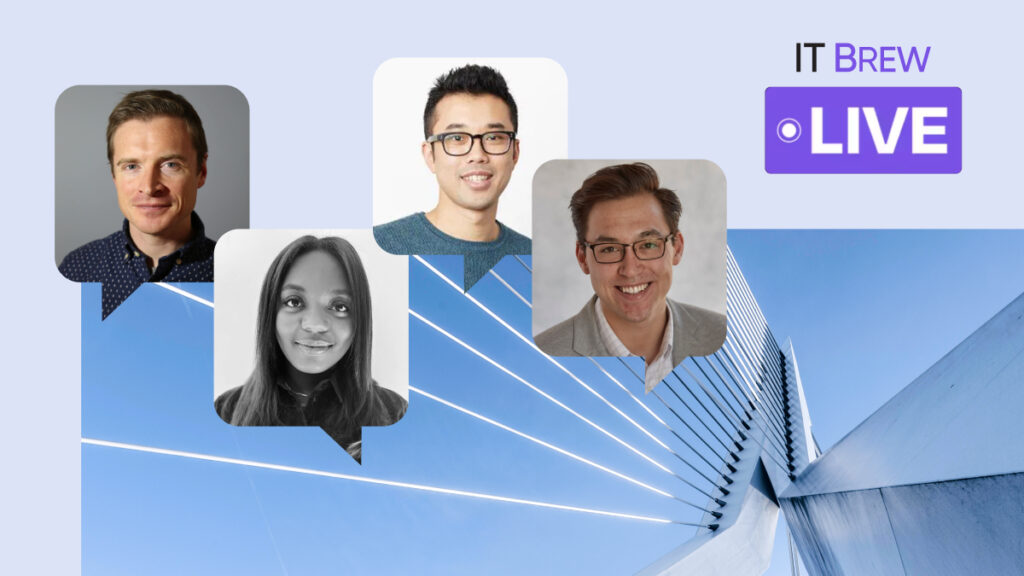







Thoropass sat down with IT Brew to discuss IT solutions powering the newest era of digital health compliance. During the virtual event, leaders in the industry, including HITRUST expert, Jason Kor, and Jim Chou, CTO of Helix, discussed the current world of compliance and InfoSec regarding health tech and digital health solutions. Also included were tidbits on the latest in all things privacy and fraud mitigation and prevention and how IT is evolving to meet ever-growing demands.
You can watch the complete discussion here. We have also highlighted some of the key takeaways from the discussion below.
Consequences of a cybersecurity breach
Compromises of technology are increasing and have reached the HealthTech sector. HealthTech organizations can store data on millions of people, which poses a risk. Risks are categorized into three major groups.
– Breach of confidentiality
– Breach of integrity
– and Availability of sensitive systems and data
As a result, compliance and cybersecurity tech companies have emerged to mitigate these liabilities.
Tools, technologies, and your team
HIPAA and SOC 2 come to mind as a baseline for health compliance. For international considerations, there’s ISO 27001. So when it comes to compliance, there is a tablescapes aspect and how you manifest and check those boxes for security. With HIPAA and SOC 2, it’s necessary to implement them at your healthcare company to show your security standards.
There can be various certifications and attestations, but it’s about staying compliant past those. Your team needs to understand why this is important, and hiring team members with that built-in understanding that protecting data is vital. This makes it easier for your company to continue to do business ethically. Additionally, there needs to be an emphasis on the spirit of the policies and frameworks to create a security culture to further your health compliance.