
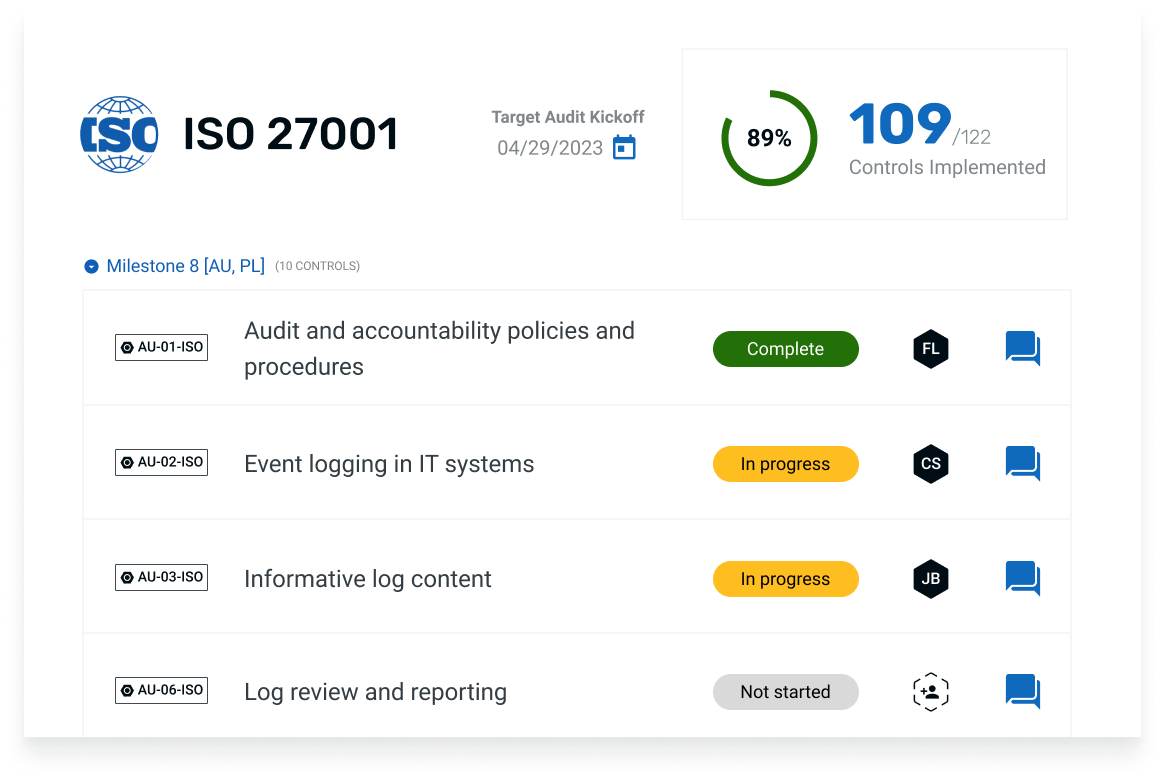






When securing an organization’s information, ISO 27001 and 27002 are critical standards but serve different purposes. Companies often grapple with choosing between them or understanding how they complement each other.
At a high level, ISO 27001 focuses on requirements for creating a certified ISMS, while ISO 27002 is a reference for implementing robust security controls.
This blog post aims to clarify both standards’ critical distinctions and practical applications, giving you the insight needed to empower your information security strategy.
Key takeaways
- ISO 27001 is a management standard for setting up an ISMS and can lead to certification, while ISO 27002 offers detailed guidelines on security controls without a certification process.
- ISO 27001 focuses on the broader framework and risk assessment for information security management, whereas ISO 27002 provides in-depth advice on implementing specific security measures.
- Both ISO 27001 and ISO 27002 can be implemented concurrently to align security controls with organizational goals and enhance risk management despite the challenges one may face during the process.
What is ISO 27001?
ISO 27001 is a recognized standard for international information security management. It sets out the criteria for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). It applies to any international organization that wants to keep its information safe.
An ISMS aims to help organizations manage and protect their information assets, ensuring the confidentiality, integrity, and availability of sensitive information.
ISO 27001 provides a systematic approach to managing information security, involving a risk management process to identify, assess, and treat information security risks. The standard covers various aspects of information security, including:
- Organizational policies
- Physical security
- Human resources security
- Access control,
- Cryptography, and more.
What is ISO 27002?
While ISO 27001 specifies the requirements for establishing, implementing, maintaining, and improving an ISMS, ISO 27002 provides a set of guidelines and best practices for implementing the controls specified in ISO 27001.
At a high level, ISO 27002 provides:
- Guidance on how to implement controls: It provides detailed guidance on implementing the control objectives outlined in Annex A of ISO 27001. Annex A is a list of 114 controls categorized into 14 sections, covering various aspects of information security.
- Information security best practices: Offers recommendations and best practices for implementing security controls in areas such as information security policies, organization of information security, human resource security, physical and environmental security, communication and operations management, access control, information systems acquisition, development, and maintenance, and more.
- Flexibility in implementation: ISO 27002 is not mandatory but is designed to be flexible. Organizations can tailor the guidance to suit their specific needs and risk environment.
- Continuous improvement: Encourages organizations to regularly review and update their information security controls to adapt to changes in technology, threats, and the business environment.
ISO 27002 serves as a valuable resource for organizations looking to implement the controls outlined in ISO 27001 effectively. It provides practical advice and guidelines to help organizations establish a robust and comprehensive information security framework aligned with international best practices.
Key distinctions between ISO 27001 and ISO 27002
As may already be clear, it’s not so much one standard versus the other as much as understanding how one standard enhances and furthers the other. Let’s look at the key distinctions between the two.
Certification status
The primary distinction lies in the fact that ISO 27001 revolves around certification. Once you’ve implemented the standard, you can get an official certification to show your compliance.
Obtaining ISO 27001 certification involves several steps, including:
- Getting the organization ready
- Setting up a management framework
- Putting security processes and controls in place
- Performing internal audits
- Having a management review
- Pursue an audit with an accredited ISO 27001 governing body
Completing these steps will help your organization achieve compliance with ISO 27001 certification. Once you cross the finish line, you’ll have a certification that not only boosts your reputation but also improves your business connections and protects your data.
Depth of detail
The depth of detail is another key difference between ISO 27001 and ISO 27002.
While ISO 27001 provides a general framework for managing information security, ISO 27002 takes it a step further by offering a more detailed guide on implementing specific security controls within that framework.
Think of ISO 27001 as the backbone, providing the structure and best practices for systematic and cost-effective information security. ISO 27002, on the other hand, is the muscle that adds strength to the structure, offering detailed advice on choosing information security controls. Together, they form a robust ISMS.
Risk assessment approach
ISO 27001 mandates a risk assessment to identify security threats as part of the certification process. An internal audit can confirm that your risk assessment process is comprehensive and effective.
On the other hand, ISO 27002 does not necessitate a risk assessment. It provides a detailed guide for implementing security controls without the need for certification.