






The General Data Protection Regulation (GDPR) is a comprehensive data protection law that governs how organizations handle personal information within the EU.
GDPR certification demonstrates your organization’s commitment to protecting personal data, according to the EU’s strict standards. While it’s not mandatory, certification can significantly enhance your organization’s credibility.
In this blog post, we’ll explore the key steps, the role of accredited certification bodies, and the strategic advantages of being GDPR-certified.
Key takeaways
- GDPR certification is a voluntary accreditation that affirms your organization’s adherence to the EU’s data protection standards, enhancing trust and competitiveness.
- Certification bodies are accredited entities that assess and certify compliance with GDPR. Certifications require renewal every three years to maintain validity.
- A systematic approach, including a gap analysis and implementing technical and organizational measures, is crucial to preparing for GDPR compliance and certification.
Understanding GDPR certification
Being GDPR compliant is mandatory for those operating within the EU, but achieving GDPR certification is not. So why would you bother? While there isn’t a European Data Protection Seal at the EU level, certification demonstrates your organization’s commitment to data privacy and security. Certification, in turn, can be used to your advantage in marketing materials and beyond, enhancing trust with stakeholders and providing a competitive edge.
So, what does it take to get certified? In short, certification involves a detailed evaluation by an accredited body, which assesses whether an organization’s data handling practices meet GDPR requirements. This process may include steps like:
- A gap analysis to identify areas for improvement
- Implementation of necessary technical and organizational measures
- Possibly, the appointment of a Data Protection Officer (DPO) to oversee compliance
GDPR certification is valid for three years, after which organizations must renew to prove ongoing compliance. It is a tangible asset for organizations to validate their dedication to protecting personal data, potentially simplifying processes for data processors and increasing overall transparency.
The role of certification bodies
Certification bodies play a crucial role in the GDPR certification process. They are accredited by supervisory authorities to evaluate and certify that organizations meet the requirements of GDPR. Their assessments are thorough, examining an organization’s data protection policies and practices to ensure compliance with the regulation.
The Member States, the supervisory authorities, the Board and the Commission shall encourage, in particular at Union level, the establishment of data protection certification mechanisms and of data protection seals and marks, for the purpose of demonstrating compliance with this Regulation of processing operations by controllers and processors.
To become a certification body, an organization must demonstrate its independence, expertise, and the establishment of clear procedures to avoid conflicts of interest. The certifications they provide are valid for three years, after which an organization must renew its certification to continue demonstrating its commitment to GDPR compliance.
Certification bodies are important because they help organizations understand what is required for GDPR certification. They don’t just assess organizations but also guide them in maintaining high data protection standards, assuring stakeholders that the organization’s data handling is trustworthy.
The benefits of being GDPR-certified
There are numerous advantages to obtaining GDPR certification. It is a testament to an organization’s unwavering dedication to safeguarding data privacy, building trust with consumers and partners, and streamlining compliance efforts, especially for data processors.
In a digital landscape fraught with security breaches, having GDPR certification is like reinforcing your ship; it mitigates the chances of data leaks and bolsters an organization’s standing as a sentinel of information security.
The perks of being GDPR-certified include:
- Serving as a bulwark against data protection issues
- Offering a distinct advantage in the marketplace and marking your organization as one that prioritizes data privacy and adheres to GDPR standards
- Potentially securing a spot on public registers maintained by the European Data Protection Board
- Enhancing your organization’s reputation
- Easing the repetitive process of assessments and audits for data processors
- Providing tangible and authoritative evidence of compliance
GDPR certification serves as a beacon, directing organizations through the complex seas of data protection. It not only offers protection from the repercussions of non-compliance but also propels them to the forefront, marking them as entities that take the privacy rights of their clientele to heart.
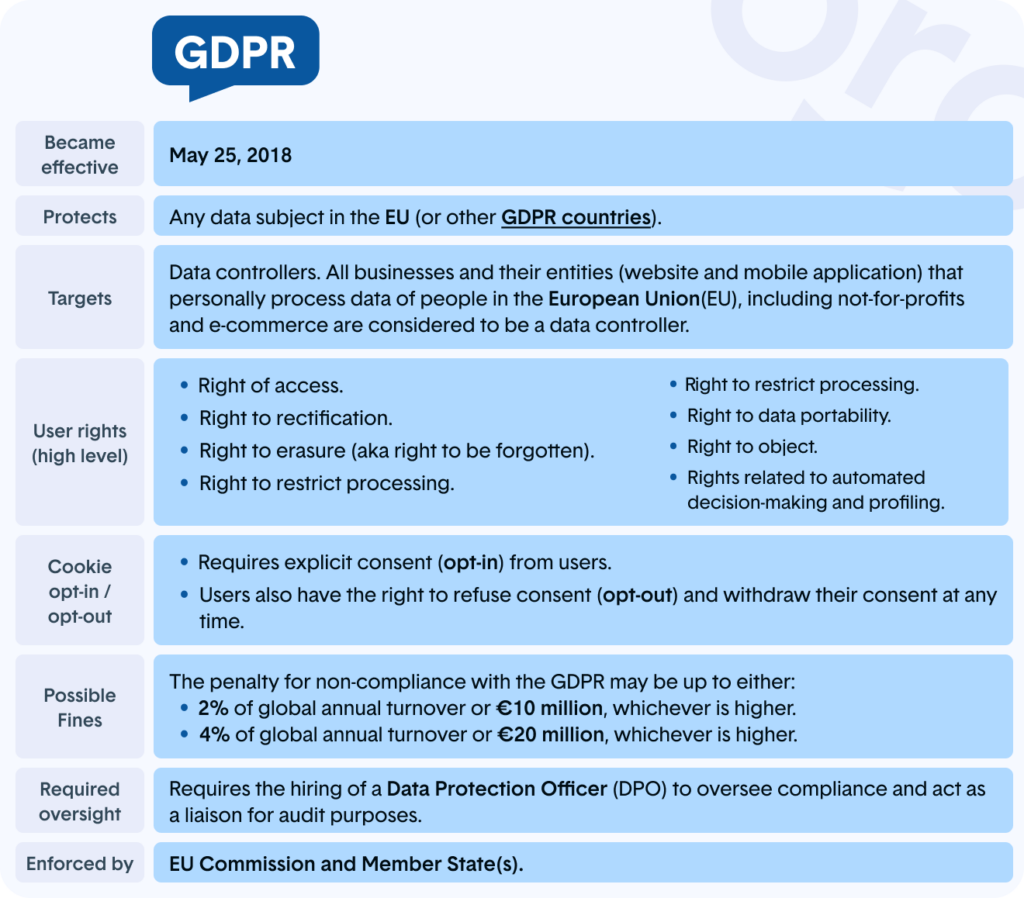
Your path to GDPR compliance: A structured approach
Embarking on the journey to GDPR certification requires a structured and methodical approach. Before setting sail, organizations must first:
- Identify the specific regulations that pertain to their operations
- Lay out a map of the structured compliance pathway that will be followed
- Create a comprehensive project plan detailing the steps to certification
This structured approach is essential, as it allows for an in-depth readiness assessment that gauges the current state of compliance and involves key stakeholders in effectively addressing GDPR obligations.
Conducting a gap analysis
Before beginning the certification process, the first step is to check your organization’s current data protection practices and see where they might not fully meet GDPR standards. This check is called a gap analysis.
Once you know the problems, you need to document them and prioritize the most important fix. The gap analysis helps you focus on the biggest issues and plan out how to tackle them one by one. With a clear list of what needs to be done, you can start working on fixing each issue, moving your organization closer to being fully compliant with GDPR.
Doing a gap analysis is more than just a paperwork exercise, however. It’s a strategic step that helps you prepare for getting certified. It gives you a clear picture of what needs to change, so when you make those changes, you know they’re the right ones that will help you meet all the GDPR requirements.
Implementing technical and organizational measures
As the journey to GDPR compliance continues, implementing technical and organizational measures becomes a pivotal step. From basic technical controls like Cyber Essentials to organizational measures such as visitor registration, each action is a strategic move to fortify your vessel against common data security failures.
Physical safeguards such as secure locks and alarm systems must be paired with organizational measures that ensure data is not only protected but respected. Organizations must also maintain a record of these measures, including data access requests, as required by Article 32(1) of the GDPR.
A business continuity plan is like your organization’s lifeboat, outlining how to manage incidents and establish recovery processes, ensuring that the organization can recover swiftly from any breach.
These measures are not static; they evolve with emerging technologies like artificial intelligence, requiring continuous adaptation and vigilance. They are the proof of an organization’s readiness to not only meet GDPR compliance but to exceed expectations, ensuring that personal data is not just stored but safeguarded with the utmost integrity.
Engaging a Data Protection Officer (DPO)
Navigating GDPR compliance is a complex endeavor that necessitates expertise and vigilance. Engaging a Data Protection Officer (DPO) is like having an experienced navigator on board, which is essential for charting the correct course and avoiding the pitfalls of non-compliance.
It’s also important to note that depending on your organization’s nature, scale, and/or scope, a DPO may be a mandatory requirement under GDPR.